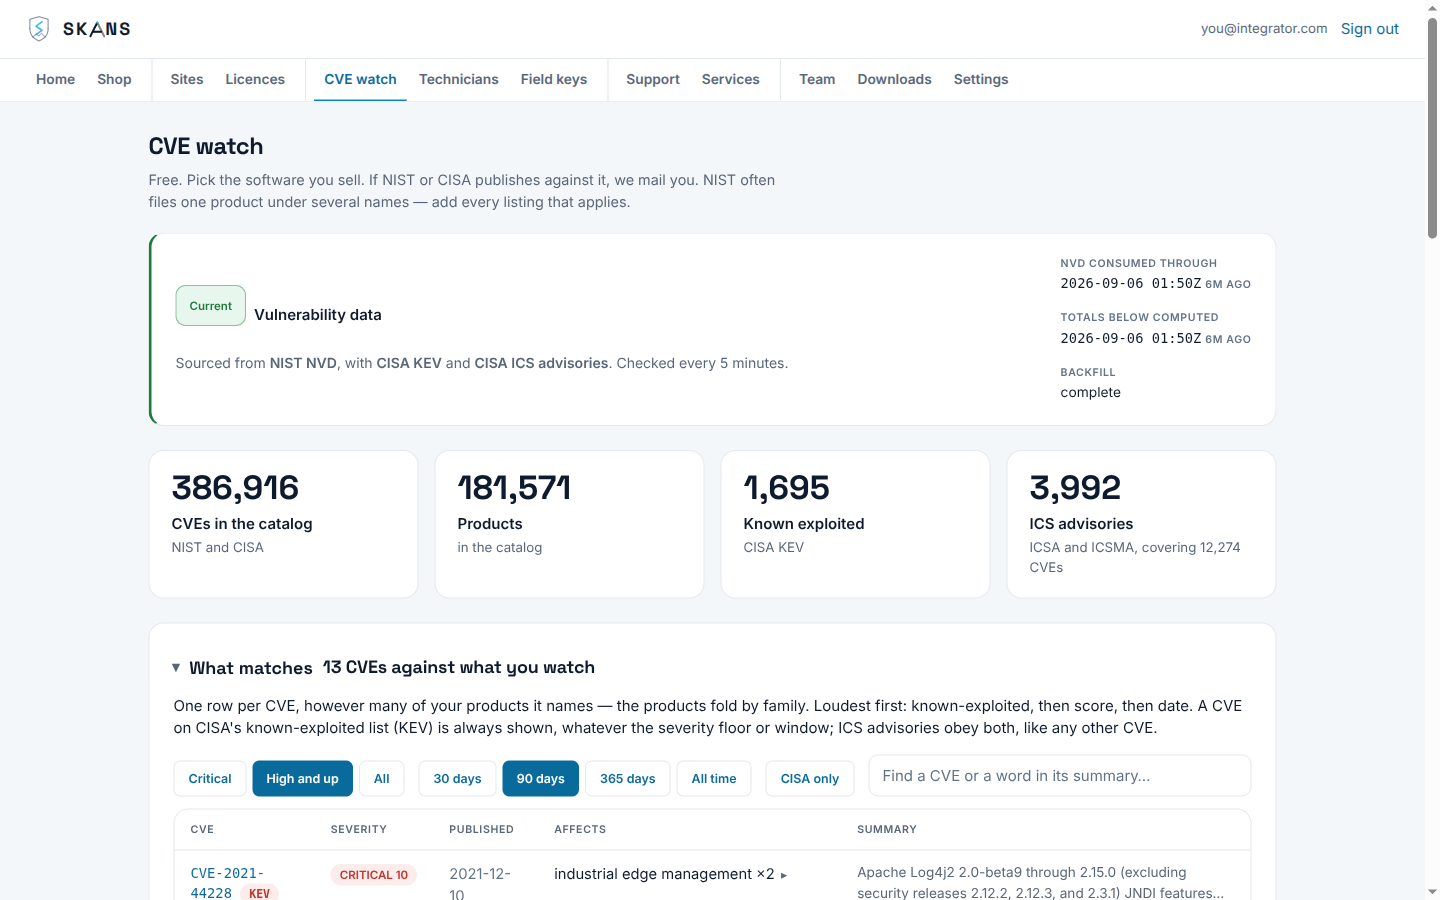
CVE Watch is live, and it's free: know the day a CVE names a product you sell
Today we’re opening CVE Watch to everyone. It is the alerting service we built for the people who sell and service the gear, and it is free.
Pick the vendors and products you carry: cameras, access controllers, PLCs, building controllers, switches, servers. When a new CVE, a CISA Known Exploited Vulnerability (KEV) entry or an ICS advisory names one of them, you get an email that day. Not a quarterly PDF, not a headline your customer reads first.
Who it’s for #
Most CVE tooling is written for the security team that owns the network. CVE Watch is written for everyone else in the chain, the people whose phone rings when a headline lands.
- Integrators and installers. You put the cameras and PLCs in. You are the first call. Know before the customer does and walk in with the answer.
- Sales teams and resellers. A Critical or KEV entry on a line you carry is a reason to call every account running it, with a fix, an upgrade, or an appliance that patches it on-site.
- OT, facilities and building teams. Watch the exact controllers, BMS heads and drives on your floor. ICS advisories land in your inbox the day they publish.
- MSPs and service desks. Watch the whole stack your customers run and triage from one list, filtered to the last 30 days, Critical only, or actively exploited only.
How it works #
- Sign up free. An email and password, or sign in with Google, Microsoft or GitHub. No card, no appliance, no sales call.
- Watch what you sell. Search a vendor or a product and add it. Watch a whole vendor (every Siemens product) or one line (a single camera family). Family spellings are matched for you.
- Get the alert. An email the day a CVE, KEV entry or ICS advisory names a watched product, plus a digest on your schedule. Open the portal to filter by window, severity, KEV and ICS.
Stop any time. Unwatch a product or switch alerts off in one click.
What’s behind it #
CVE Watch runs on the vulnerability index Skans Labs maintains for its on-site appliance: the public CVE List, the CISA KEV catalog and the CISA ICS advisory feed, joined to a vendor and product catalogue. As of today that is:
| CVEs, with CVSS severity on every record | 386,916 |
| CISA Known Exploited Vulnerabilities | 1,695 |
| ICS and medical advisories | 3,992 |
| Products | 181,571 |
| Vendors | 37,660 |
Two rules worth knowing. A KEV entry always shows, whatever severity filter you set, because exploited is exploited. And the match follows the CVE’s own affected-product list, so a watch on a vendor catches every product under it and a watch on one product family catches only that family.
And when the alert lands #
CVE Watch tells you a product you sell is exposed. The Skans appliance is what closes it, on the customer’s network, without that network ever touching the internet. It matches the same corpus against each device’s installed version, routes the fix into approved patch rings, and files the evidence against NIST 800-171 and CMMC. The Community edition is free, and every edition has every capability.
Already have a Skans portal account? CVE Watch is already yours. Open CVE Watch in the portal and add your first vendor.